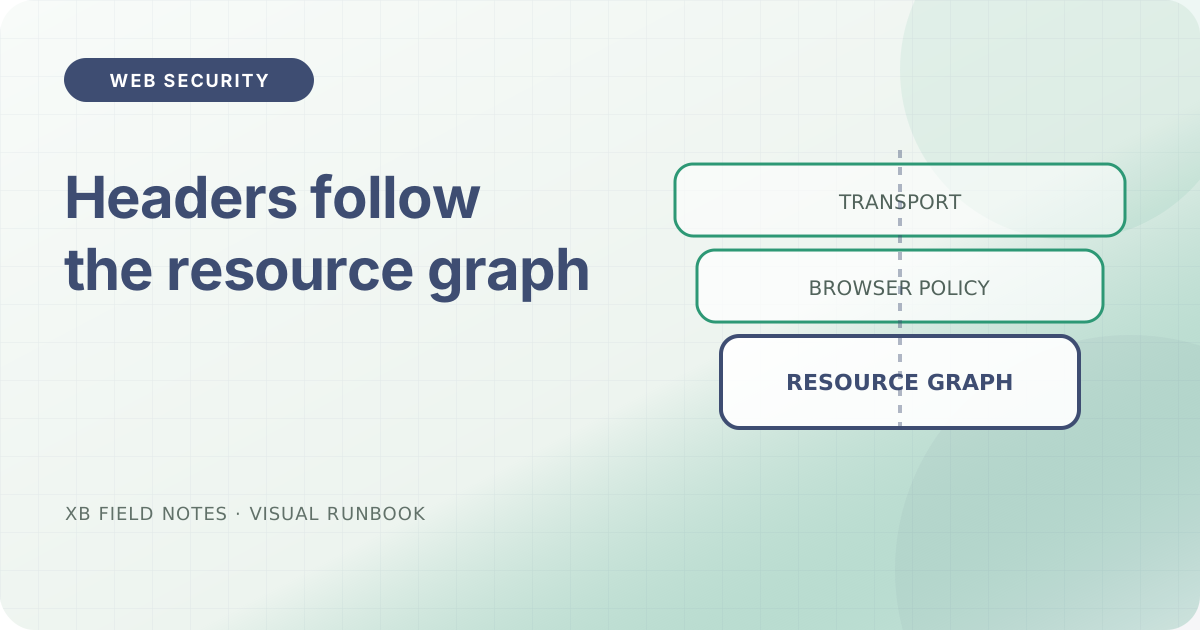
Transport, browser policy, and resource graph shown as security layers.

Security headers should describe the actual page

Start with a narrow policy, then expand it only when a documented feature needs another resource.
July 23, 2026 · 2 min · XB Field Notes
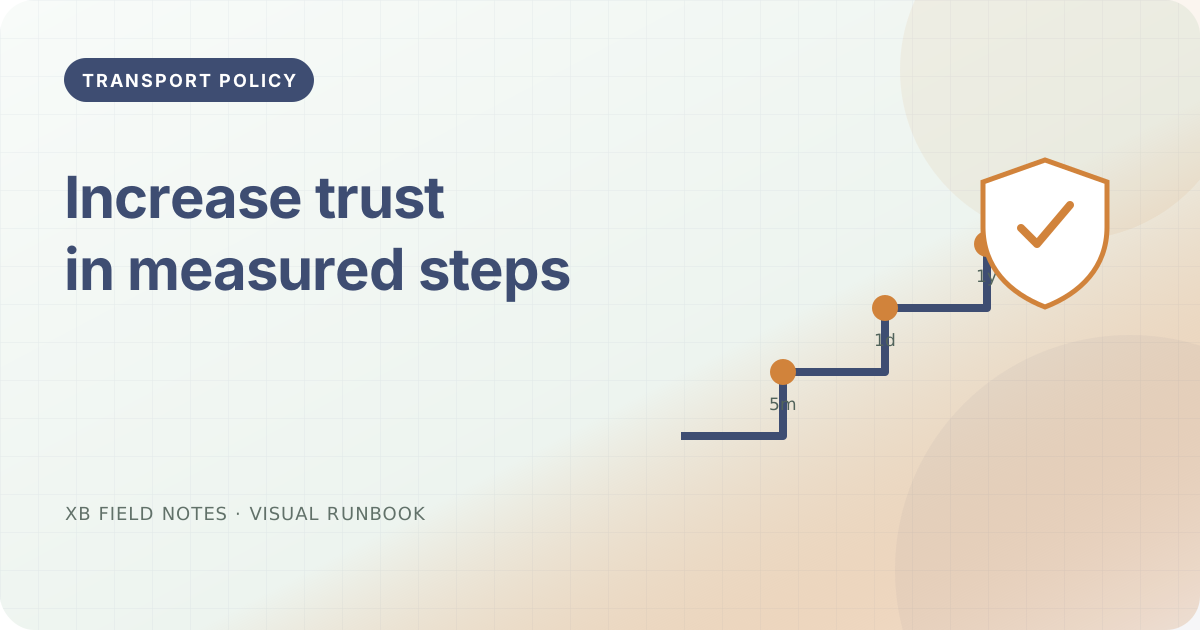
An HSTS policy increasing through staged max-age steps before covering subdomains.

HSTS should be rolled out with a recovery plan

HSTS is cached browser policy, so a configuration mistake can outlive the server change that created it.
June 23, 2026 · 2 min · XB Field Notes
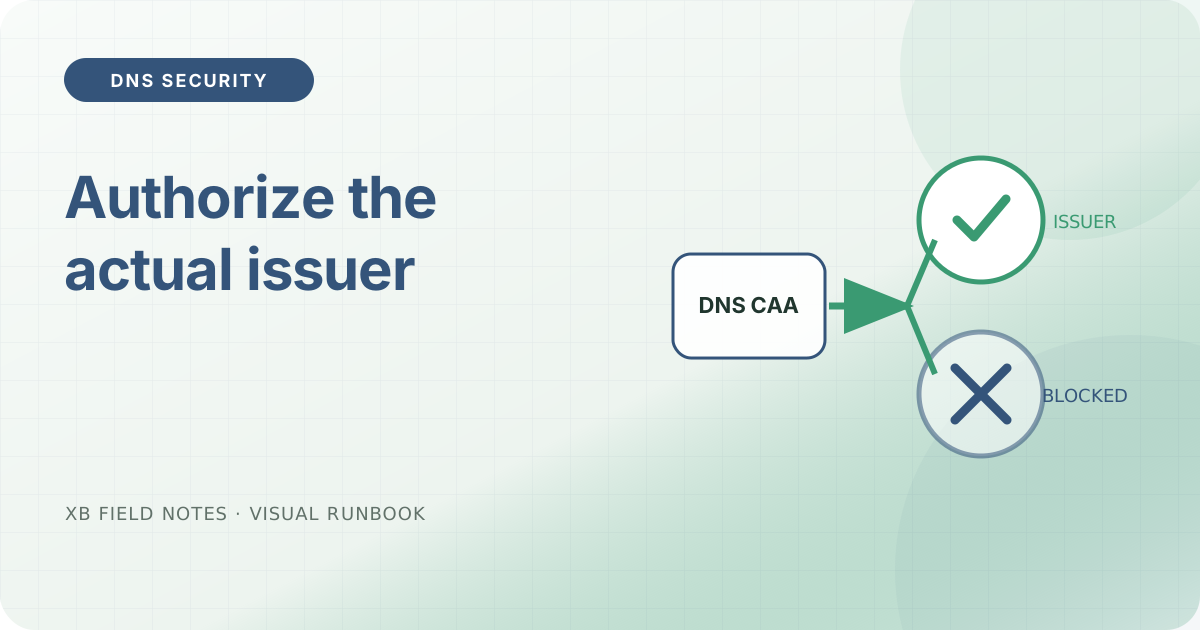
A DNS policy record authorizing one certificate authority while rejecting another.

CAA records should authorize the issuer you actually use

CAA narrows certificate issuance policy, but a mistaken record can block renewal as effectively as an expired certificate.
June 17, 2026 · 2 min · XB Field Notes
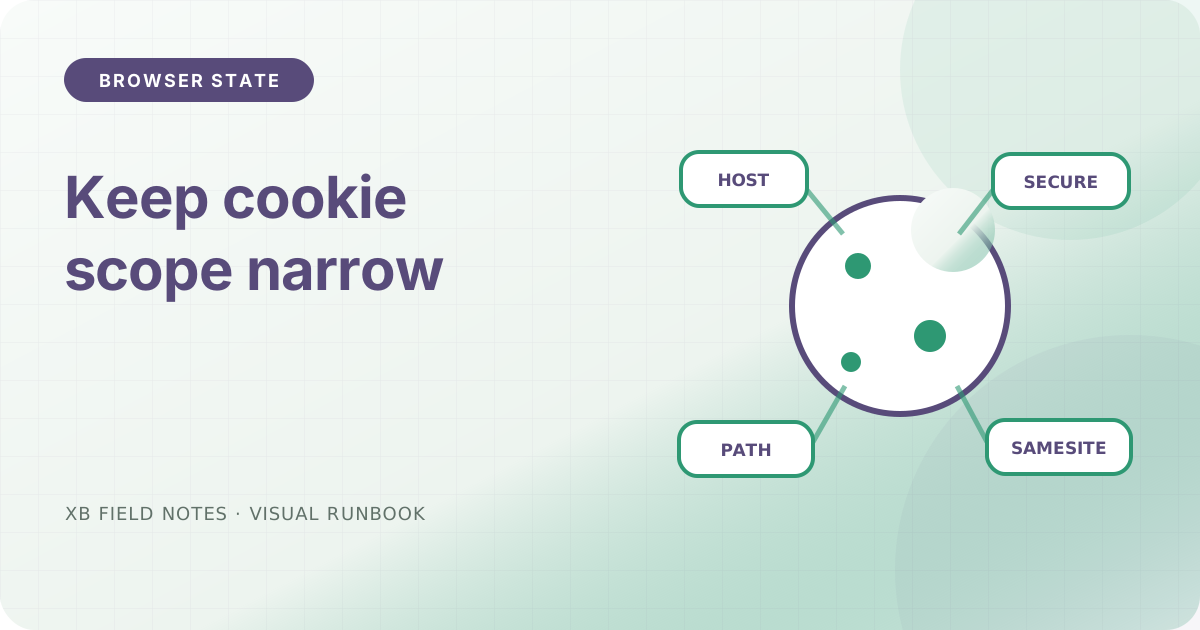
A browser cookie constrained by host, path, transport, and same-site boundaries.

Cookie scope should be narrower than the application boundary

A cookie sent to more hosts or paths than necessary enlarges the impact of every mistake at those boundaries.
June 15, 2026 · 2 min · XB Field Notes
A file representation passing through a media-type label before reaching a browser.

Content-Type should describe the bytes you actually send

A filename is only a hint; the response header is the browser-facing contract for the representation.

June 11, 2026 · 2 min · XB Field Notes