Observe-decide-act boxes beside the message: Check the dates, verify the chain.

A TLS certificate expiry is a date you can read

A certificate’s expiry is a deadline for certificate validation, not a timer that necessarily closes every existing connection. Read the certificate actually served to the intended hostname, then distinguish its validity window from the rest of the trust decision. A future notAfter date alone does not establish that HTTPS is healthy. ...
June 22, 2026 · 5 min · XB Field Notes
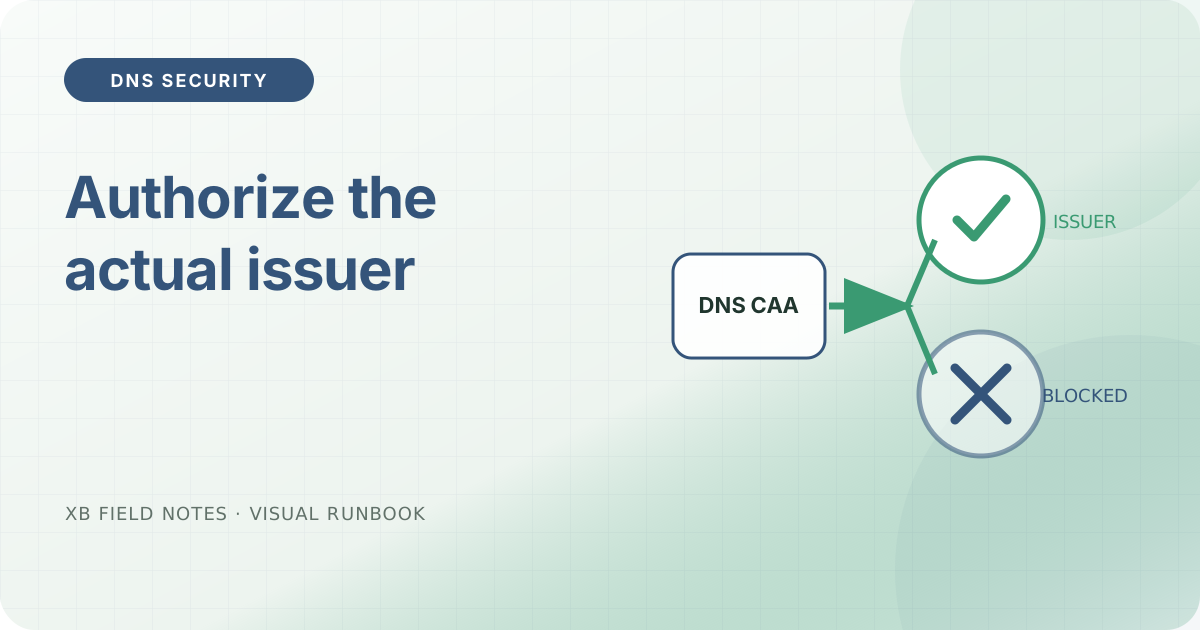
A DNS policy record authorizing one certificate authority while rejecting another.

CAA records should authorize the issuer you actually use

CAA narrows certificate issuance policy, but a mistaken record can block renewal as effectively as an expired certificate.

June 17, 2026 · 2 min · XB Field Notes
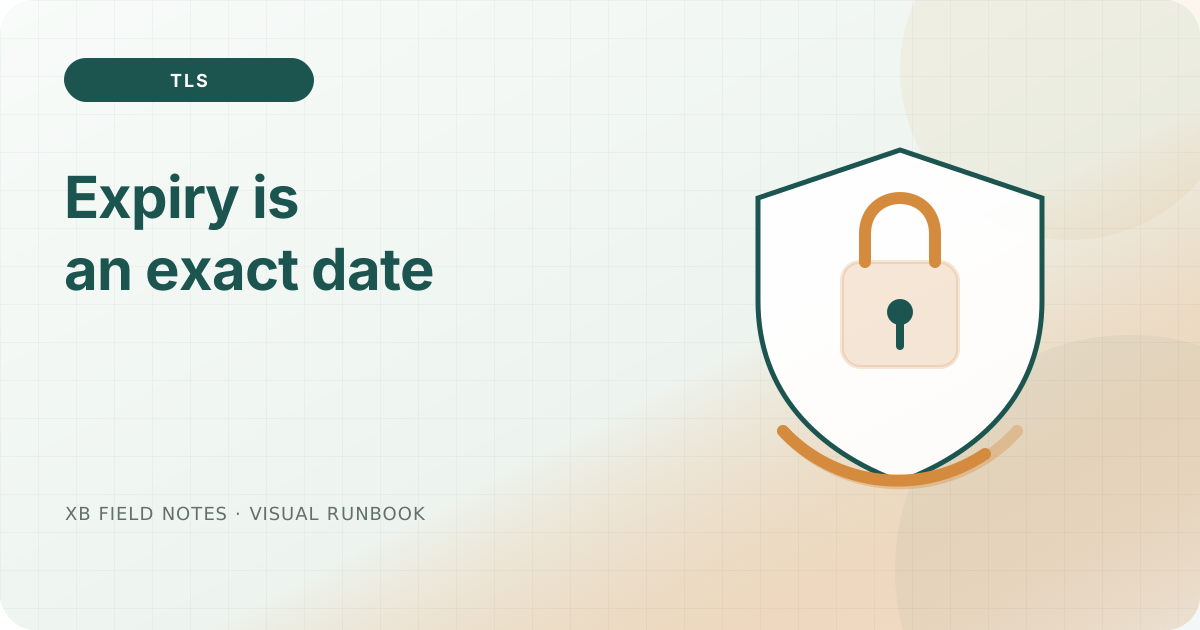
A certificate shield with a validity and expiry gauge.

Certificate expiry is a date, not a dashboard color

Use SNI, inspect the public certificate, and alert before renewal becomes an incident.

June 10, 2026 · 2 min · XB Field Notes
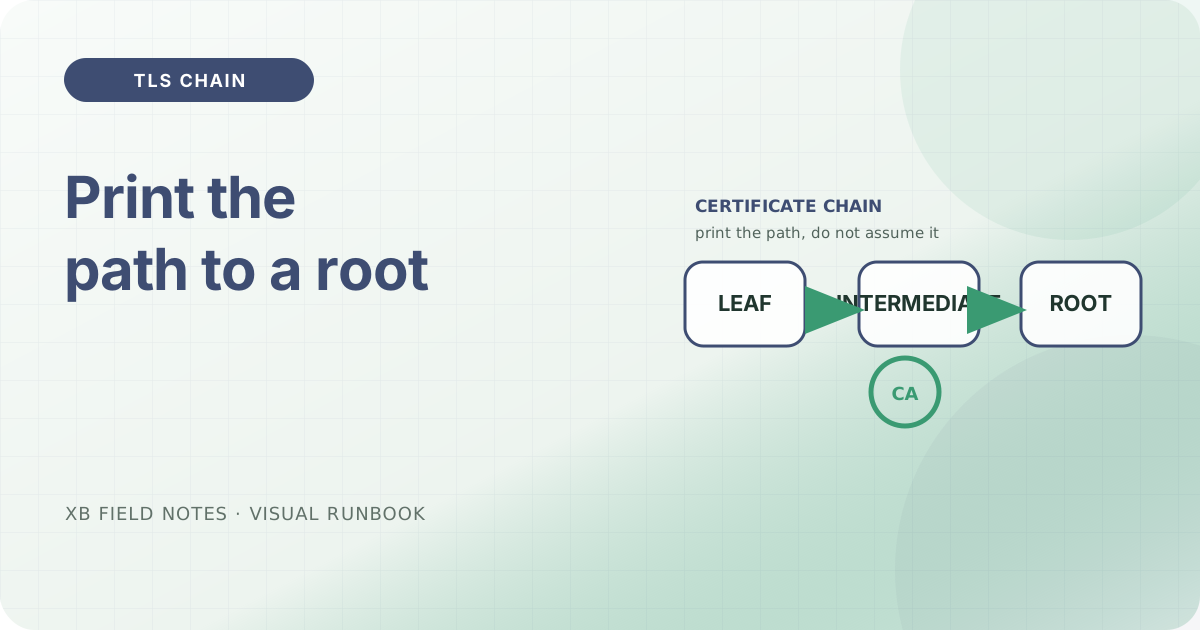
A leaf certificate connected through an intermediate to a trusted root, with each link naming the issuer.

A certificate chain is a path you should be able to print

Read the chain the edge actually presents, not just the leaf, before you trust the rollout.

June 8, 2026 · 3 min · XB Field Notes