An article heading beside linked OBSERVE, DECIDE, and ACT boxes, a circular pointer, and guide lines.

Least privilege is a threshold, not a feeling

Least privilege means granting a principal the operations required for a defined job, on the intended resources, for an appropriate lifetime. It is a testable policy rather than a reassuring label. Start with the service’s real launch identity and dependencies; an unused permission and a missing permission are different findings that need different responses. ...
August 11, 2026 · 5 min · XB Field Notes
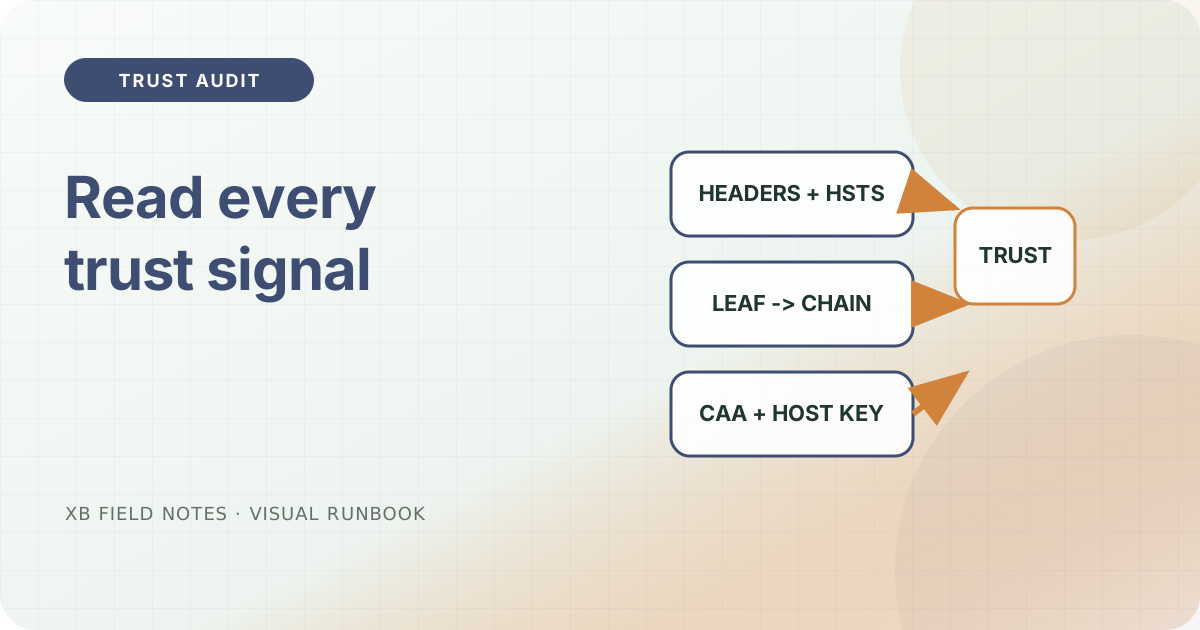
A trust inventory of a public edge, from headers and TLS identity to certificate chain and CAA.

Audit the trust of a public edge

Inspect security policy, verified TLS identity, issuance restrictions, and deployment trust with explicit limits.

August 6, 2026 · 7 min · XB Field Notes
Observe-decide-act boxes beside the message: TLS 1.3 handshake, verify the identity.

TLS 1.3 handshake basics

TLS 1.3 establishes traffic keys and authenticates the peer under the application’s trust policy. Ordinary HTTPS authenticates the server; client certificates are optional, not an automatic consequence of encryption. A successful TCP connection alone establishes neither identity nor a working HTTP service. ...

August 6, 2026 · 5 min · XB Field Notes
A recorded SSH host fingerprint connected to a key symbol.

SSH host keys are part of the deployment record

Record the expected fingerprint, use a deliberate StrictHostKeyChecking policy, and treat changes as an incident until explained.

July 28, 2026 · 2 min · XB Field Notes
An SSH key constrained to one identity and a narrow permission scope.

SSH key hygiene is mostly limiting where a key works

SSH key hygiene starts with knowing which credential grants which access, who owns it, and how that access ends. A key comment helps people maintain an inventory, but it is not an authenticated owner record or an authorization rule. Track fingerprints alongside accountable owners, intended accounts, permitted operations, and a removal plan. Generating a modern key is only the beginning. ...

July 6, 2026 · 5 min · XB Field Notes
Article title beside three connected panels labeled Observe, Decide, and Act.

A firewall policy must match the packet path, family, and chain order

A firewall applies packet policy at particular points in a network stack. A useful rule therefore names more than a port: its address family, hook, direction, state conditions, and place among other rules matter. With nftables, base chains attach to Netfilter hooks at specified priorities. The effective packet path, rather than the order of descriptions in an operations document, determines which decisions a packet encounters. ...

July 1, 2026 · 6 min · XB Field Notes
Article title beside three connected panels labeled Observe, Decide, and Act on a pale grid.

Harden a systemd service by testing its boundaries

Service hardening should turn a specific unwanted operation into a denied operation while preserving the work the application must perform. systemd supplies execution settings for filesystem views, namespaces, privileges, and other resources. They are separate controls with separate limits. Adding four familiar directives does not make every readable file, reachable process, inherited descriptor, or allowed system call disappear. ...

June 27, 2026 · 5 min · XB Field Notes